SOC Analyst Course with Splunk SIEM
Build practical skills for Security Operations Center environments. Learn security monitoring, SIEM operations, log analysis, threat detection, incident investigation and threat hunting through hands-on training with real-time devices.
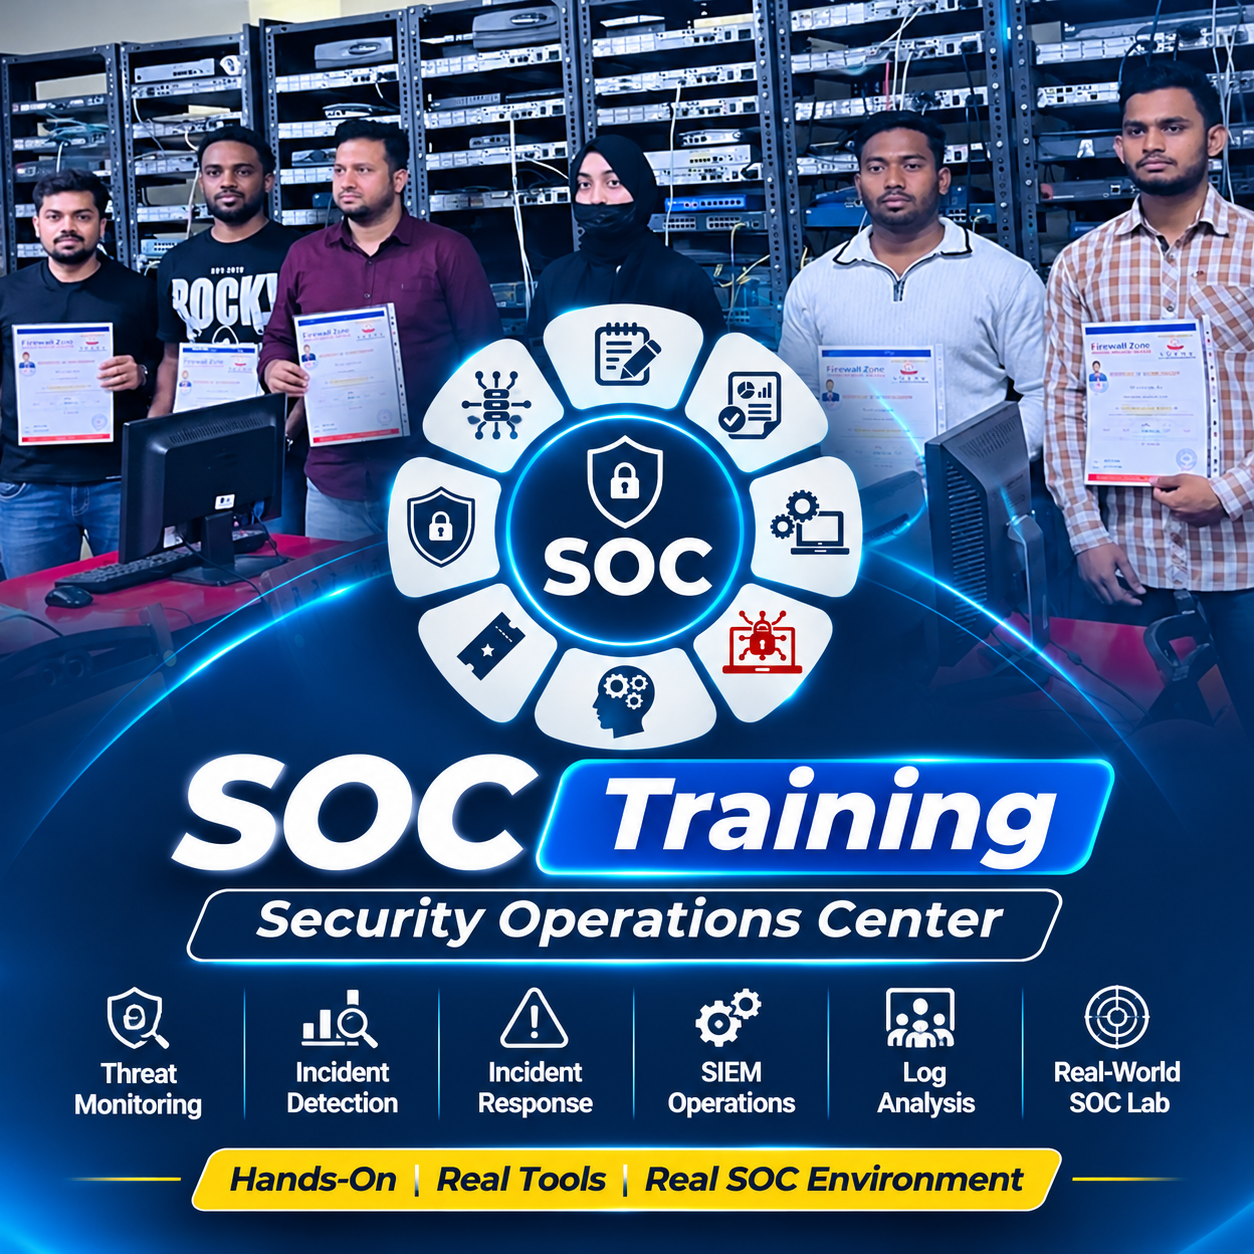
Gain hands-on experience in SOC operations through guided lab sessions covering Splunk SIEM, security monitoring, log investigation, threat detection, incident response, alert triage, and security event analysis in real-world SOC environments.
Explore Splunk installation, Universal Forwarder setup, log collection, dashboards and SIEM use cases.
SIEM TrainingUnderstand firewall logs, Windows event IDs, Sysmon logs and security event investigation.
Log InvestigationLearn security event monitoring, SIEM correlation, suspicious activity identification and threat detection.
Threat DetectionStudy threat hunting scenarios including web server scanning, brute-force activity and email analysis.
Threat HuntingPractice network fundamentals, packet inspection using Wireshark and port discovery with Nmap.
Network AnalysisUnderstand incident handling stages, security investigation and malware outbreak analysis.
Incident HandlingExplore firewall policies, security profiles, NAT, VPN configuration and network protection.
Firewall TrainingStudy endpoint security fundamentals, agent installation, detection, prevention, monitoring and reporting.
Endpoint ProtectionLearn through practical exercises. Build your understanding of Splunk SIEM, security logs, threat detection, incident handling and SOC operations.
Explore the complete course curriculum covering SOC operations, Splunk SIEM, ethical hacking, network security, firewall security, endpoint security and network security management.
Develop practical knowledge of Security Operations Centre activities, SIEM monitoring, security log analysis, threat detection and incident response through structured classroom training and real-time lab practice.
This course is designed for beginners who want to start learning SOC operations.
Understand important SOC operations and security technologies covered in the course curriculum.
Strengthen your understanding through hands-on exercises and practical security scenarios.
The course covers skills and topics relevant to the following SOC Analyst operations roles:
Hear directly from our students about their learning experiences at Firewall Zone Institute of Technology. Discover their classroom experiences, practical training sessions, hands-on lab learning and technical skill development.
Discover a student's learning experience at Firewall Zone.
Learn about hands-on technical training and practical sessions.
Explore student experiences and technical learning journeys.
See what students share about their classroom experience.
Hear about learning technical skills through practical training.
Watch another student share their experience with Firewall Zone.
Firewall Zone Institute of Technology – Learn with practical training, real-time devices and hands-on technical experience.
Our training approach combines classroom learning, practical lab exercises and real-world network security scenarios to help learners understand the responsibilities and workflows of a Security Operations Centre.
Practise networking and security concepts through hands-on exercises using real Cisco routers and switches.
Learn through classroom training sessions guided by industry experts.
Understand practical network deployment and configuration scenarios used in network environments.
Receive personalized guidance to improve your understanding of course concepts and practical exercises.
Get additional lab practice to strengthen your understanding of technical topics and configurations.
Learn configuration methods and practical approaches aligned with industry-standard practices.
Build your foundation in SOC operations with structured training, practical security topics and guidance from experienced trainers.
Learn security monitoring, SIEM operations, log analysis and incident response through practical SOC Analyst training.
Interested in SOC Analyst Training with Splunk SIEM? Contact Firewall Zone Institute of Technology for course details, classroom training information and upcoming batch schedules.
Visit our institute in Mehdipatnam, Hyderabad, for enquiries about SOC Analyst Training and classroom learning.
Firewall Zone Institute of Technology
Opp: Pillar No: 3,
Royal Colony,
Mehdipatnam, Hyderabad,
Telangana, India.
Find answers to common questions about the SOC Analyst course, Splunk SIEM training, curriculum, practical sessions and learning requirements.
SOC Analyst Training teaches the fundamentals of Security Operations Centre activities, including security monitoring, log analysis, threat detection, SIEM operations and incident investigation.
The course covers networking for SOC analysts, SOC fundamentals, Splunk SIEM, SIEM use cases, threat handling, ethical hacking, network security, firewall security, endpoint security and security standards and auditing.
Yes. The curriculum includes Splunk installation, Universal Forwarder, log collection, dashboards, firewall logs, Windows event logs, event IDs and Sysmon analysis.
No prerequisites are specified for this course. It is listed as a beginner-level training programme.
Yes. The course is listed at beginner level and starts with networking fundamentals, SOC concepts.
The training methodology includes hands-on labs, classroom sessions, real-world network scenarios and practical exercises using real-time devices.
Topics include campus and WAN networks, OSI and TCP/IP models, protocols and ports, router configuration, packet flow, Wireshark and Nmap port identification.
Yes. The Splunk SIEM curriculum includes Windows logs, event IDs, dashboards and Sysmon analysis.
Yes. Firewall topics include zones and interfaces, virtual routers, security policies, NAT, web filtering, antivirus, IPS, DoS protection, VPN and high availability.
Yes. Endpoint security topics include fundamentals, product selection, planning and implementation, agent profiles, detection and prevention, monitoring and reporting.
Yes. The supplied curriculum includes 20 ethical hacking modules, covering topics such as reconnaissance, network scanning, enumeration, vulnerability analysis, malware threats, sniffing, social engineering, web application security, wireless security, cloud computing and cryptography.
Threat hunting involves investigating network and security activity to identify suspicious behaviour. The course includes threat-hunting use cases such as web-server scanning, brute-force activity and email address analysis.
SOC Analyst L1 and L2 are career roles listed in the course opportunities. The supplied syllabus does not provide a detailed comparison of their responsibilities.
Potential roles include SOC Analyst L1 and L2, SIEM Analyst, Security Operations Analyst, Incident Response Analyst, Threat Hunter, Security Monitoring Analyst, Network Security Analyst, Security Engineer and SOC Engineer.
Yes. Classroom training with practical lab exposure is included in the supplied course details.
Yes. Incident handling and investigation topics are included, along with SIEM use cases and threat-handling exercises.
Yes. The curriculum includes network security concepts, monitoring, event management, log-server topics and network security management.
The batch date provided for this course is 23rd November 2026. Please contact the institute to confirm the latest schedule and availability.
Firewall Zone Institute of Technology is located at Opp: Pillar No: 3, Royal Colony, Mehdipatnam, Hyderabad, Telangana, India.
Contact Firewall Zone Institute of Technology by calling 040-23530263 or by sending a WhatsApp message to +91 88861 92132 for course enquiries.
Connect with Firewall Zone Institute of Technology for course details, batch schedules and enrolment enquiries.
Expert support and industry-leading training in CCNA RS, CCNP Security, Networking, and Cyber Security Courses, empowering individuals with the skills to achieve independence, career growth, and technical excellence.
© 2026 Firewall Zone Institute of IT